

PoA 模块架构
概述
权益证明授权(PoA)许可型共识模块是一个 Cosmos SDK 模块,它实现了一种许可型共识机制,由指定的管理员控制验证者集合。与传统的权益证明系统不同,PoA 验证者是由管理权限显式授权和管理的,而不是根据质押代币来选择。目录
- 架构
- 管理员控制流
- 验证者生命周期
- 费用分配 → 参见 distribution.md
- 治理 → 参见 governance.md
- 技术实现
- 安全注意事项
架构
SDK 集成点
PoA 模块作为标准 staking 模块的替代方案接入 Cosmos SDK,提供一种替代性的共识机制: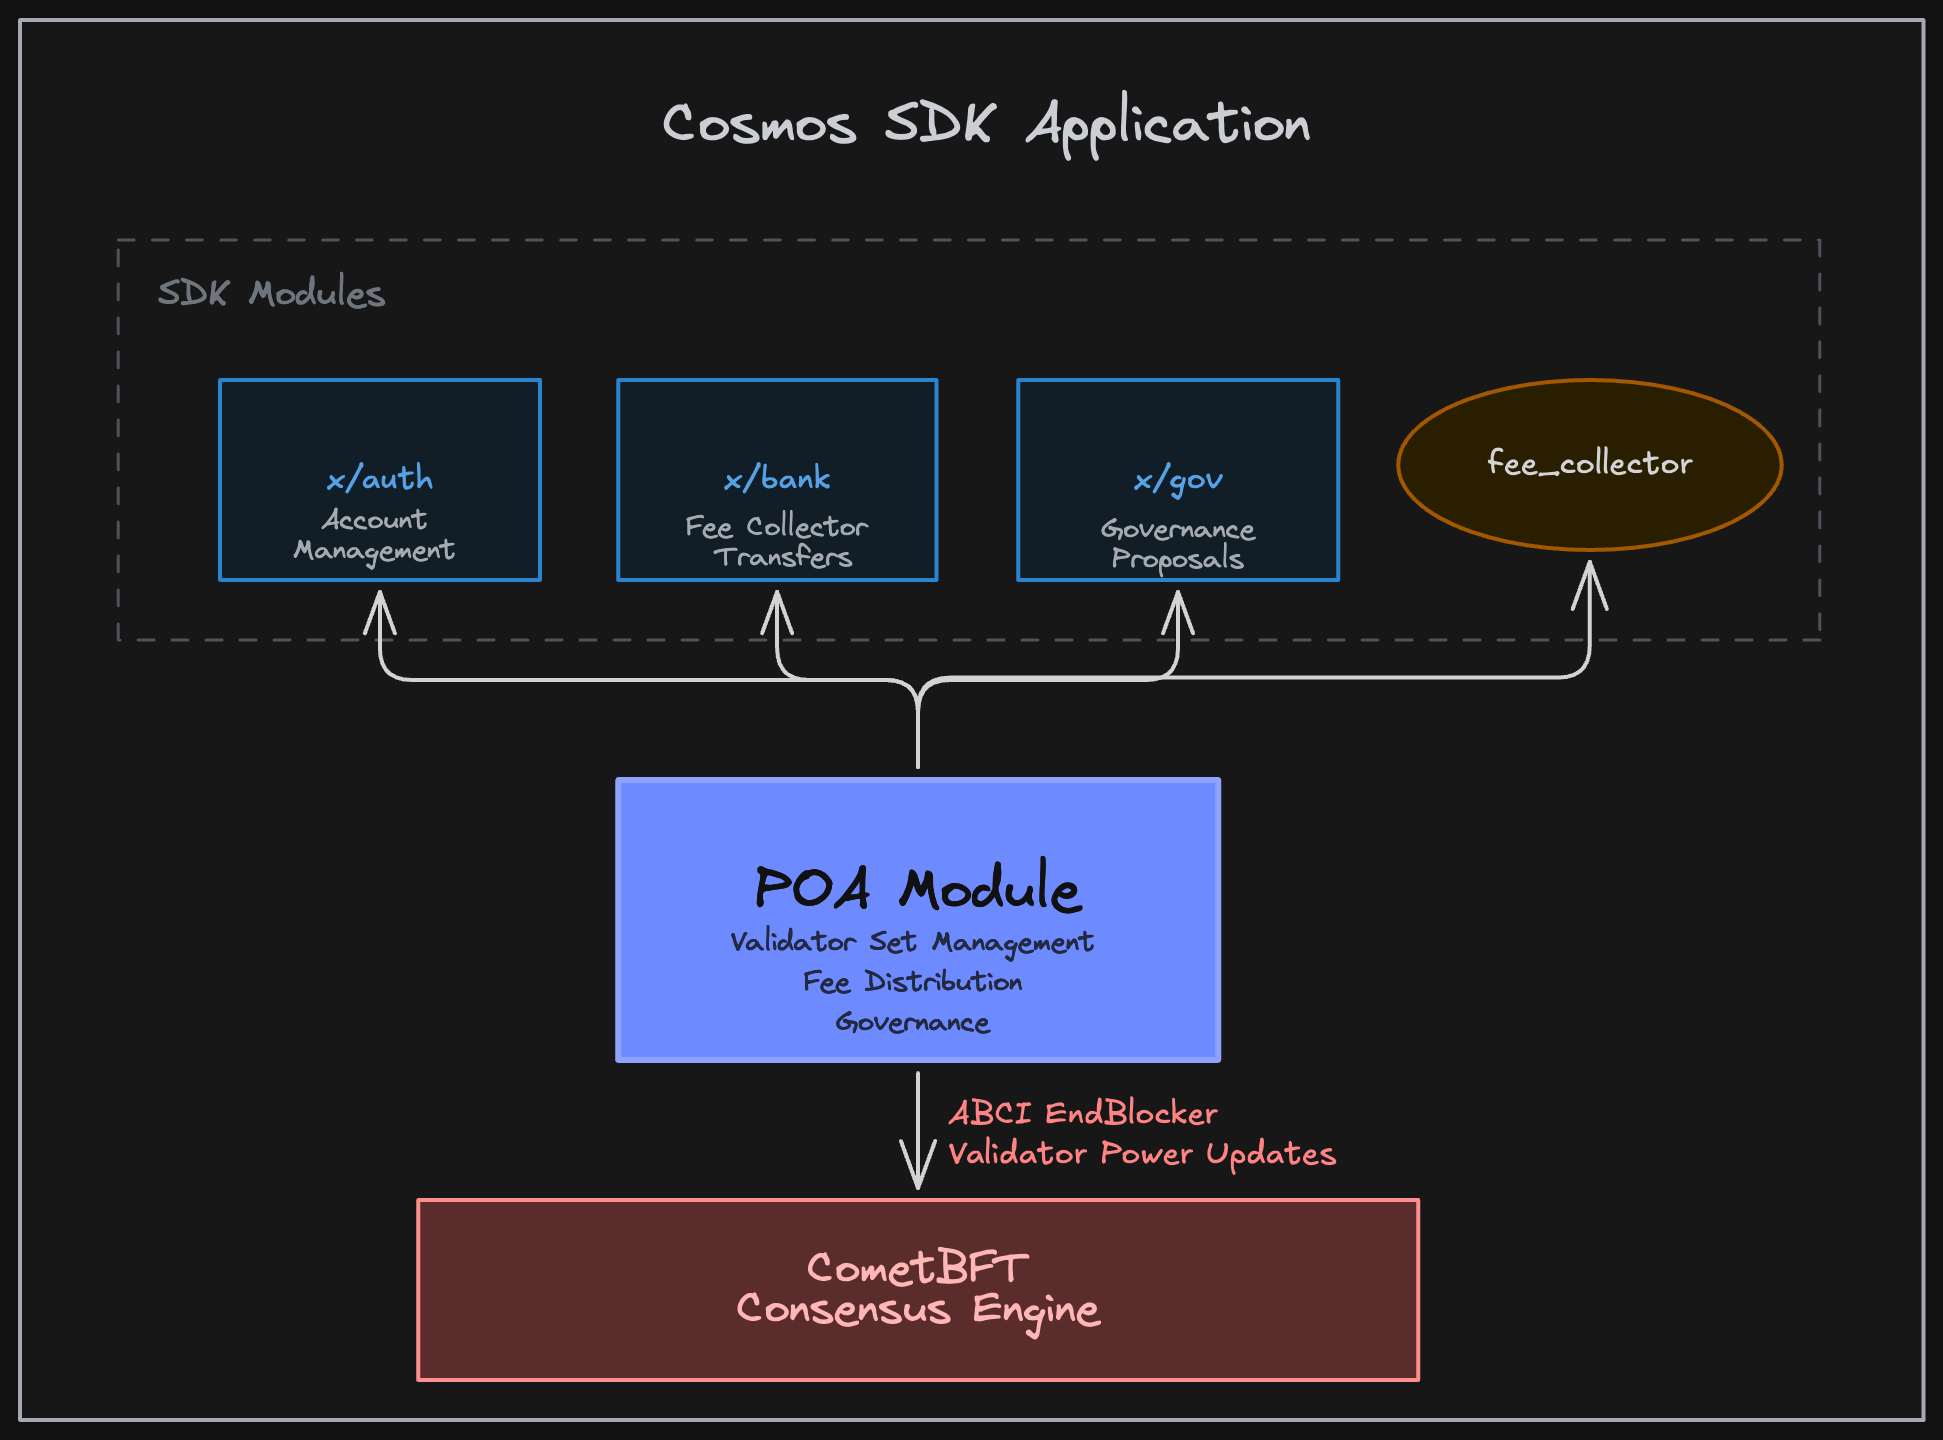 上图展示了 PoA 模块如何与 Cosmos SDK 模块(x/auth、x/bank、x/gov)、fee_collector 账户以及 CometBFT 共识引擎集成。
关键集成点:
- 替代 x/staking:PoA 提供验证者管理能力,但不包含代币委托或绑定
- 与 x/gov 集成:自定义治理钩子确保只有活跃验证者可以参与,并且 tally 函数覆盖会将投票权重分配给验证者权重(详情)
- 使用 x/auth 和 x/bank:为费用分配提供标准账户和代币管理(详情)
- ABCI 生命周期:实现
EndBlocker以向 CometBFT 传递验证者更新(详情)
架构决策
由管理员控制的验证者集合 与根据代币权重决定验证者的权益证明不同,PoA 使用单一管理员地址来授权验证者。这个设计选择:- 支持验证者身份已知的许可型网络
- 取消验证者参与的代币要求(无需代币绑定)
- 将信任集中于管理员地址(参见安全注意事项)
- 费用通过自定义 ante handler 路由到 PoA 模块账户(完整细节参见 Fee Routing Setup)。
- 费用按验证者权重比例分配(而不是按委托质押)
- 验证者按需提取费用
- 完整细节参见费用分配
- 只有活跃验证者(权重 > 0)可以提交、存入或投票提案
- 投票权重由验证者权重决定,而不是由代币持有量决定
- 防止非验证者参与治理
- 实现细节参见治理
cosmossdk.io/collections 和复合键结构:
- 主键:
(power, consensus_address)支持按权重排序的高效迭代 - 在共识地址和操作员地址上建立二级索引以实现快速查询
- 当权重变化时需要重新设置键,但无需单独排序
- 技术细节参见存储设计
管理员控制流
设置管理员权限
PoA 模块由一个在创世时配置的管理员地址控制。该管理员拥有以下排他权限:- 更新验证者权重(授予或撤销共识参与资格)
- 修改模块参数
- 批量更新整个验证者集合
x/poa/types/keys.go:10(params 前缀)
只有管理员自身可以通过参数变更来更新自己。
管理验证者集合
MsgUpdateValidators (x/poa/keeper/msg_server.go:72)
管理员可以通过一笔交易批量更新验证者:
- 身份认证:交易必须由管理员地址签名
- 校验:每个验证者更新都会校验以下内容:
- 有效的公钥
- 非负权重
- 有效的元数据(操作员地址、moniker、description)
- 没有重复的操作员地址
- 权重变化:任何权重变化都会触发:
- 费用检查点(在权重变化前分配待处理费用)
- 总权重重新计算
- ABCI 验证者更新队列
- 共识更新:变更会在当前区块结束时生效
更新参数
MsgUpdateParams (x/poa/keeper/msg_server.go:26)
管理员可以更新模块参数(当前仅包括管理员地址本身)。这要求:
- 交易由当前管理员签名
- 对新参数进行校验
验证者生命周期
验证者注册
MsgCreateValidator (x/poa/keeper/msg_server.go:45)
无许可创建:任何地址都可以注册为验证者候选人:
-
提交注册:提供公钥和元数据
- PubKey:Ed25519
- Operator Address:将接收费费用并管理该验证者的账户
- Moniker:人类可读名称(最多 256 个字符)
- Description:附加详情(最多 256 个字符)
-
初始状态:新创建的验证者初始 power = 0,直到管理员通过
MsgUpdateValidators更新它- 不参与共识
- 不赚取费用
- 不能参与治理投票
x/poa/keeper/validator.go:95
获得共识权重
验证者只能通过管理员操作获得共识权重:- 管理员更新权重:通过
MsgUpdateValidators - 权重 > 0:验证者变为活跃状态
- ABCI 更新:CometBFT 在下一个区块将验证者加入活跃集合
- 费用资格:验证者开始按比例累积费用
- 治理权利:验证者可以提交提案、存款并投票
- 权重是表示投票权重的整数
- 更高权重 = 更大的共识影响力和费用份额
- 管理员可以向上或向下调整权重
- 将权重设为 0 会把验证者移出共识,但不会删除该验证者
x/poa/keeper/validator.go:19
移除验证者
软移除(移除权重):- 管理员将验证者权重设为 0
- 验证者仍保持已注册状态,但不再活跃
- 后续管理员可以重新激活该验证者
- 验证者条目会保留在验证者映射中
费用分配
PoA 模块实现了一个自定义的基于检查点的费用分配系统,按照验证者权重比例分配区块费用。 关键特性:- 费用累积在 PoA 模块账户 中
- 在检查点按验证者权重比例分配
- 检查点会在权重变化或提取时触发
- 验证者按需提取已累积的费用
- 使用 DecCoins 提高精度,防止零头累积
x/poa/keeper/distribution.go
治理
PoA 模块将治理参与限制为仅活跃验证者,并使用验证者权重而不是已绑定代币作为投票权重。 关键特性:- 使用现有的 x/gov 模块
- 只有活跃验证者(权重 > 0)可以提交、存入或投票提案
- 投票权重等于验证者权重
- 自定义 tally 函数替代标准治理计票逻辑
- 管理员通过权重分配间接控制治理
x/poa/keeper/governance.go 和 x/poa/keeper/hooks.go
技术实现
存储设计
Collections Schema (x/poa/types/keys.go)
该模块使用 cosmossdk.io/collections 实现类型安全的状态管理:
| 前缀 | 集合 | 键类型 | 值类型 | 用途 |
|---|---|---|---|---|
| 0 | params | - | Params | 管理员地址和模块配置 |
| 1 | validators | (int64, string) | Validator | 主映射,按权重排序 |
| 2 | validator_by_consensus | string | (int64, string) | 索引:共识地址 → 复合键 |
| 3 | validator_by_operator | string | (int64, string) | 索引:操作员地址 → 复合键 |
| 4 | total_power | - | int64 | 所有验证者权重之和 |
| 5 | total_allocated | - | ValidatorFees | 已分配费用总和 |
x/poa/keeper/keeper.go:16
ABCI 集成
EndBlocker (x/poa/keeper/abci.go:9)
该模块通过 ABCI 与 CometBFT 共识集成:
- 权重变化:当验证者权重变化时,创建
ValidatorUpdate - 队列更新:将更新存储到内存队列中
- EndBlock:在区块结束时,返回所有排队的更新
- CometBFT 处理:共识引擎将更新应用到下一个区块
- 清空队列:返回后清空队列
x/poa/module.go:128
安全性考虑
-
单一控制点:
- 管理员地址控制整个验证者集合
-
验证者注册:
- 任何人都可以注册为验证者候选人
- 只有管理员可以授予共识权重
-
总权重不变量:
- 总权重必须始终 > 0
- 防止因零权重导致链停滞
- 每次通过检查点触发器调整权重时都会执行校验
-
治理限制:
- 只有活跃验证者(权重 > 0)才能参与
- 防止未授权用户发送治理垃圾信息
- 确保治理代表真实的共识参与者
-
验证者索引:
- 唯一的共识地址可防止重复验证者
- 唯一的操作员地址可防止费用混淆
PoA Module Architecture
Overview
The Proof of Authority (PoA) permissioned consensus module is a Cosmos SDK module that implements a permissioned consensus mechanism where a designated admin controls the validator set. Unlike traditional Proof of Stake systems, PoA validators are explicitly authorized and managed by an administrative authority rather than being selected based on staked tokens.Table of Contents
- Architecture
- Admin Control Flow
- Validator Lifecycle
- Fee Distribution → See distribution.md
- Governance → See governance.md
- Technical Implementation
- Security Considerations
Architecture
SDK Integration Points
The PoA module plugs into the Cosmos SDK as a replacement for the standard staking module, providing an alternative consensus mechanism:
The diagram above shows how the PoA module integrates with Cosmos SDK modules (x/auth, x/bank, x/gov), the fee_collector account, and CometBFT consensus engine.
Key Integration Points:
- Replaces x/staking: PoA provides validator management without token delegation or bonding
- Integrates with x/gov: Custom governance hooks ensure only active validators can participate and tally function override allocates vote weight to validator power (details)
- Uses x/auth & x/bank: Standard account and token management for fee distribution (details)
- ABCI Lifecycle: Implements
EndBlockerto communicate validator updates to CometBFT (details)
Architectural Decisions
Admin-Controlled Validator Set Unlike proof-of-stake where validators are determined by token weight, PoA uses a single admin address to authorize validators. This design choice:- Enables permissioned networks with known validator identities
- Removes token requirement from validator participation (no token bonding required)
- Centralizes trust in the admin address (see Security Considerations)
- Fees are routed to the PoA module account via a custom ante handler (see Fee Routing Setup for complete details).
- Fees allocated proportionally to validator power (not delegated stake)
- Validators withdraw fees on-demand
- See Fee Distribution for complete details
- Only active validators (power > 0) can submit, deposit, or vote on proposals
- Voting weight determined by validator power, not token holdings
- Prevents non-validator governance participation
- See Governance for implementation details
cosmossdk.io/collections with a composite key structure:
- Primary key:
(power, consensus_address)enables efficient power-sorted iteration - Secondary indexes on consensus and operator addresses for fast lookups
- Requires re-keying when power changes, but eliminates need for separate sorting
- See Storage Design for technical details
Admin Control Flow
Setting Admin Authority
The PoA module is controlled by a single admin address configured at genesis. This admin has exclusive authority to:- Update validator power (grant/revoke consensus participation)
- Modify module parameters
- Batch update the entire validator set
x/poa/types/keys.go:10 (params prefix)
Only the admin can update itself with a parameter change.
Managing Validator Set
MsgUpdateValidators (x/poa/keeper/msg_server.go:72)
The admin can batch update validators through a single transaction:
- Authentication: Transaction must be signed by the admin address
- Validation: Each validator update is validated for:
- Valid public key
- Non-negative power
- Valid metadata (operator address, moniker, description)
- No duplicate operator addresses
- Power Changes: Any power change triggers:
- Fee checkpoint (allocates pending fees before power changes)
- Total power recalculation
- ABCI validator update queue
- Consensus Update: Changes take effect at the end of the current block
Updating Parameters
MsgUpdateParams (x/poa/keeper/msg_server.go:26)
The admin can update module parameters (currently only the admin address itself). This requires:
- Transaction signed by current admin
- Validation of new parameters
Validator Lifecycle
Validator Registration
MsgCreateValidator (x/poa/keeper/msg_server.go:45)
Permissionless Creation: Any address can register as a validator candidate:
-
Submit Registration: Provide public key and metadata
- PubKey: Ed25519
- Operator Address: Account that will receive fees and manage the validator
- Moniker: Human-readable name (max 256 chars)
- Description: Additional details (max 256 chars)
-
Initial State: Created validators have power = 0 until the admin updates it via
MsgUpdateValidators- Not participating in consensus
- Not earning fees
- Cannot vote in governance
x/poa/keeper/validator.go:95
Gaining Consensus Power
Validators can only gain consensus power through admin action:- Admin Updates Power: Via
MsgUpdateValidators - Power > 0: Validator becomes active
- ABCI Update: CometBFT adds validator to active set at next block
- Fee Eligibility: Validator starts accumulating fees proportionally
- Governance Rights: Validator can submit proposals, deposit, and vote
- Power is an integer representing voting weight
- Higher power = more consensus influence and fee share
- Power can be adjusted up or down by admin
- Setting power = 0 removes validator from consensus without deleting
x/poa/keeper/validator.go:19
Removing Validators
Soft Removal (Removing power):- Admin sets validator power to 0
- Validator remains registered but inactive
- Can be reactivated by admin later
- Validator entry is preserved in the map of validators
Fee Distribution
The PoA module implements a custom checkpoint-based fee distribution system that allocates block fees proportionally to validator power. Key Features:- Fees accumulate in the PoA module account
- Allocated proportionally to validator power at checkpoints
- Checkpoints triggered by power changes or withdrawals
- Validators withdraw accumulated fees on-demand
- Uses DecCoins for precision to prevent dust accumulation
x/poa/keeper/distribution.go
Governance
The PoA module restricts governance participation to active validators only, using validator power as voting weight instead of bonded tokens. Key Features:- Uses existing x/gov module
- Only active validators (power > 0) can submit, deposit, or vote on proposals
- Voting weight equals validator power
- Custom tally function replaces standard governance tallying
- Admin indirectly controls governance through power distribution
x/poa/keeper/governance.go and x/poa/keeper/hooks.go
Technical Implementation
Storage Design
Collections Schema (x/poa/types/keys.go)
The module uses cosmossdk.io/collections for type-safe state management:
| Prefix | Collection | Key Type | Value Type | Purpose |
|---|---|---|---|---|
| 0 | params | - | Params | Admin address and module config |
| 1 | validators | (int64, string) | Validator | Primary map, sorted by power |
| 2 | validator_by_consensus | string | (int64, string) | Index: consensus addr → composite key |
| 3 | validator_by_operator | string | (int64, string) | Index: operator addr → composite key |
| 4 | total_power | - | int64 | Sum of all validator power |
| 5 | total_allocated | - | ValidatorFees | Sum of allocated fees |
x/poa/keeper/keeper.go:16
ABCI Integration
EndBlocker (x/poa/keeper/abci.go:9)
The module integrates with CometBFT consensus through ABCI:
- Power Changes: When validator power changes, create
ValidatorUpdate - Queue Updates: Store updates in memory queue
- EndBlock: At end of block, return all queued updates
- CometBFT Processing: Consensus engine applies updates for next block
- Clear Queue: After returning, clear the queue
x/poa/module.go:128
Security Considerations
-
Single Point of Control:
- Admin address controls entire validator set
-
Validator Registration:
- Anyone can register as validator candidate
- Only admin can grant consensus power
-
Total Power Invariant:
- Total power must remain > 0
- Prevents zero-power chain halts
- Validated on every power adjustment via a checkpoint trigger
-
Governance Restrictions:
- Only active validators (power > 0) can participate
- Prevents governance spam from unauthorized users
- Ensures governance represents actual consensus participants
-
Validator Indexing:
- Unique consensus address prevents duplicate validators
- Unique operator address prevents fee confusion